Zig
Zig
Salesforce OAuth2 Refresh Access Token
See more OAuth2 Examples
Demonstrates how to refresh a Salesforce Access Token.Note: Use Chilkat v10.1.2 or later for this example.
Chilkat Zig Downloads
const std = @import("std");
const chilkat = @import("chilkat");
pub fn main(init: std.process.Init) !void {
const alloc = init.arena.allocator();
// This example requires the Chilkat API to have been previously unlocked.
// See Global Unlock Sample for sample code.
// It is assumed we previously obtained an OAuth2 access token.
// This example loads the JSON access token file
// saved by this example: Get SalesForce OAuth2 Access Token via Authorization Flow
const json_token = try chilkat.JsonObject.init();
defer json_token.deinit();
json_token.loadFile("qa_data/tokens/_salesforce.json") catch {
std.debug.print("Failed to load _salesforce.json\n", .{});
return;
};
// This is an example of a Salesforce OAuth2 access token to be refreshed:
// {
// "access_token": "00D41000....uLZBpT6",
// "refresh_token": "5Aep....25xdGgkrV",
// "signature": "cjTbSc5DvcKpaMoRTzuQTJLb1tcMw8LEO01flq4aMD4=",
// "scope": "refresh_token id",
// "instance_url": "https://d41000000f8a0eak-dev-ed.my.salesforce.com",
// "id": "https://login.salesforce.com/id/00D41000000F8A0EAK/005410000....xAAE",
// "token_type": "Bearer",
// "issued_at": "1738348388166"
// }
const oauth2 = try chilkat.OAuth2.init();
defer oauth2.deinit();
oauth2.setTokenEndpoint("https://login.salesforce.com/services/oauth2/token");
// Replace this with your actual client ID (Consumer Key)
oauth2.setClientId("CLIENT_ID");
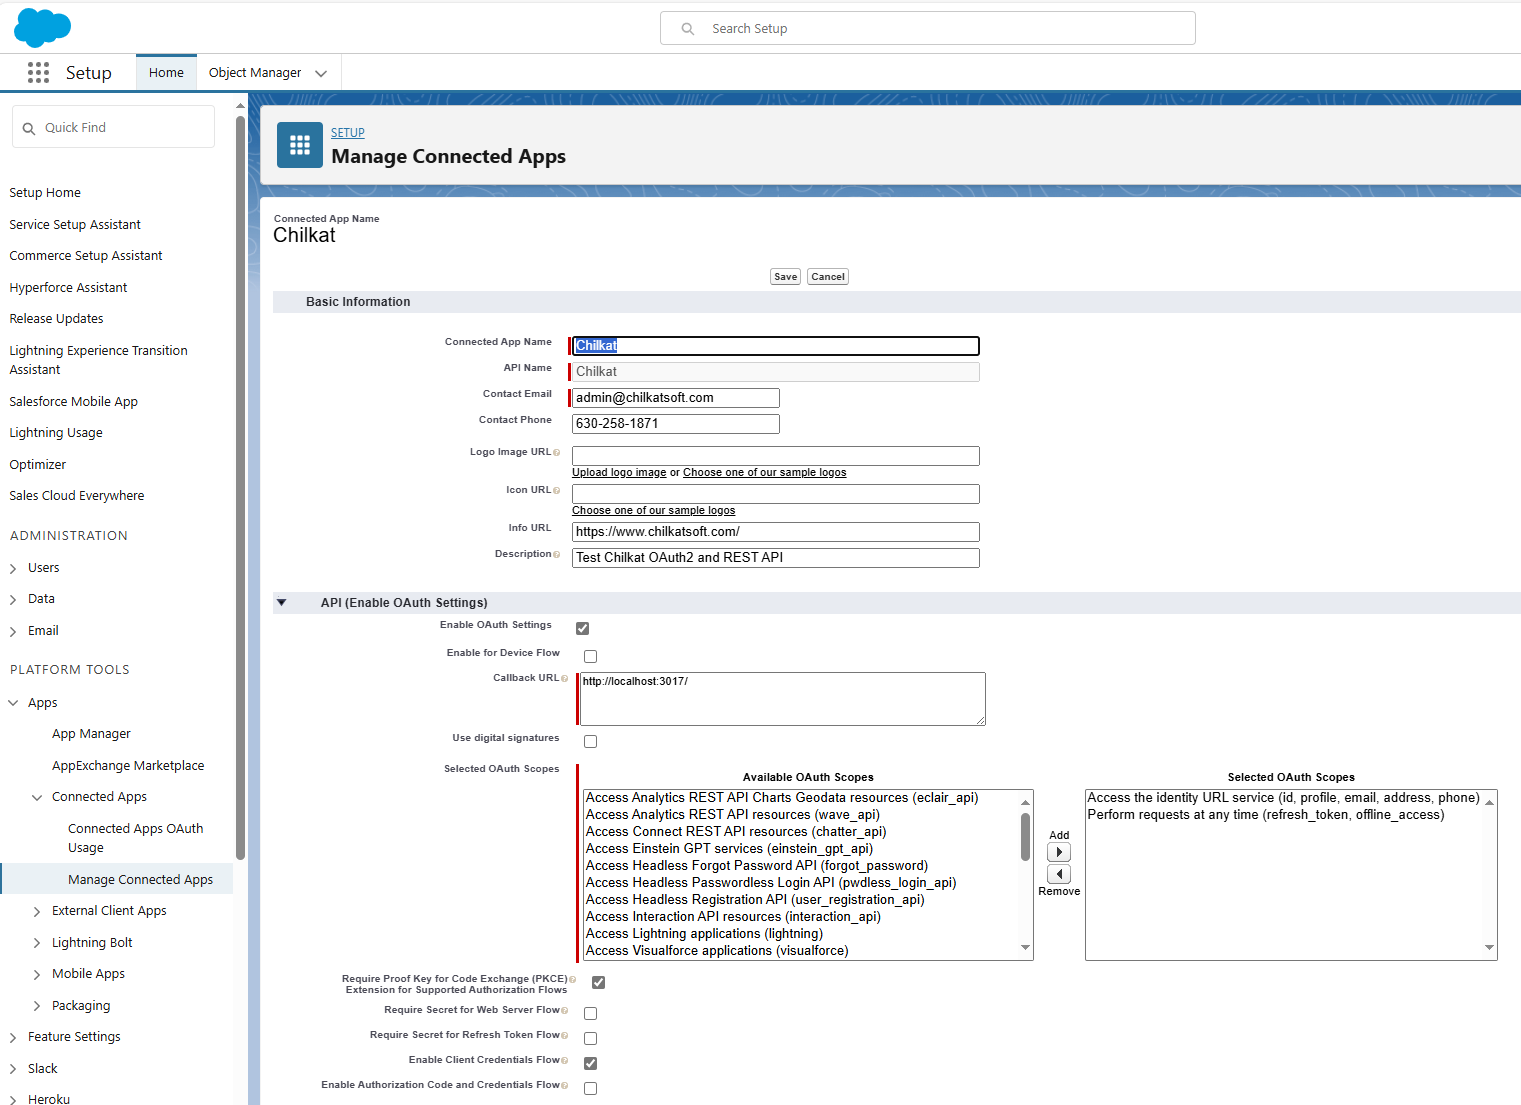
// Note: The client secret is not required because we configured our Connected App
// to not require it for the refresh flow. See the screenshot below.
// Get the "refresh_token"
oauth2.setRefreshToken(try json_token.stringOf(alloc, "refresh_token"));
// Send the HTTP POST to refresh the access token..
oauth2.refreshAccessToken() catch {
std.debug.print("{s}\n", .{try oauth2.getLastErrorText(alloc)});
return;
};
// The response contains a new access token, but we must keep
// our existing refresh token for when we need to refresh again in the future.
json_token.updateString("access_token", try oauth2.getAccessToken(alloc)) catch {};
// Save the new JSON access token response to a file.
const sb_json = try chilkat.StringBuilder.init();
defer sb_json.deinit();
json_token.setEmitCompact(false);
json_token.emitSb(sb_json) catch {};
sb_json.writeFile("qa_data/tokens/_salesforce.json", "utf-8", false) catch {};
std.debug.print("OAuth2 authorization granted!\n", .{});
std.debug.print("New Access Token = {s}\n", .{try oauth2.getAccessToken(alloc)});
// --------------------------------------------------------------------------
// Here's a screenshot of a Salesforce Connected App
// which does not requires the secret for the authorization or refresh flow.
//  }