Xbase++
Xbase++
Windows Credentials Manager - AutoSplit Larger Secrets
See more Secrets Examples
Secrets stored in the Windows Credentials Manager can be a maximum of 2560 bytes in size. If the content of the secret is too large for the Windows Credential Manager, Chilkat will automatically split the secret into parts and store a shorter JSON manifest.Note: This example requires Chilkat v10.1.0 or later.
Chilkat Xbase++ Downloads
LOCAL nSuccess
LOCAL oSecrets
LOCAL oJson
LOCAL oJsonSecret
nSuccess := 0
// This example requires the Chilkat API to have been previously unlocked.
// See Global Unlock Sample for sample code.
oSecrets := CreateObject("Chilkat.Secrets")
// The default value of AutoSplit is 1.
// Note: AutoSplit only applies when the secret location is "local_manager"
// and the app is running on the Windows OS. All other secret locations, such as Apple Keychain,
// AWS Secrets Manager, Azure Key Vault, etc. don't have limitations that are so small.
oSecrets:AutoSplit := 1
// On Windows, this is the Windows Credentials Manager
// On MacOS/iOS, it is the Apple Keychain
// (This example is explaining how a secret too large for the Windows Credential Manager
// is automatically compressed and split into parts if needed.)
oSecrets:Location := "local_manager"
// Specify the name of the secret.
// service and username are required.
// appName and domain are optional.
// Note: The values are arbitrary and can be anything you want.
oJson := CreateObject("Chilkat.JsonObject")
oJson:UpdateString("appName", "AA_MyApp")
oJson:UpdateString("service", "OAuth2")
oJson:UpdateString("domain", "onedrive")
oJson:UpdateString("username", "matt")
// Get the secret to be stored.
oJsonSecret := CreateObject("Chilkat.JsonObject")
nSuccess := oJsonSecret:LoadFile("qa_data/tokens/oneDrive.json")
IF (nSuccess == 0)
? oJsonSecret:LastErrorText
oSecrets:destroy()
oJson:destroy()
oJsonSecret:destroy()
RETURN
ENDIF
// Note: The oneDrive.json file we used for testing is 4824 bytes in size,
// which exceeds the maximum size (2560 bytes) allowed by the Windows Credentials Manager.
// When the size is too large, Chilkat will first compress the content of the secret.
// If the compressed size is small enough, then it is stored compressed without splitting.
// Otherwise the compressed data is split
// Your application does not need to know how the secret is stored in the Windows Credentials Manager.
// When fetching the secret, Chilkat automatically decompresses and re-composes from parts.
// Create or update the secret.
nSuccess := oSecrets:UpdateSecretJson(oJson, oJsonSecret)
IF (nSuccess == 0)
? oSecrets:LastErrorText
oSecrets:destroy()
oJson:destroy()
oJsonSecret:destroy()
RETURN
ENDIF
// This is the auto-split secret viewed in the Windows Credentials Manager:
// 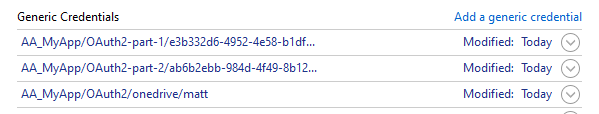 // Note: If you delete the auto-split secret by calling Chilkat's DeleteSecret method,
// the parts are automatically deleted.
// Also, if you update the secret, the old parts are automatically deleted and new parts are created.
? "Success"
oSecrets:destroy()
oJson:destroy()
oJsonSecret:destroy()