Xbase++
Xbase++
Azure Key Vault - Create or Update a JSON Secret
See more Secrets Examples
Demonstrates how to create or update a JSON secret stored in the Azure Key Vault.Note: This example requires Chilkat v10.1.0 or later.
Chilkat Xbase++ Downloads
LOCAL nSuccess
LOCAL oBootstrap
LOCAL oBsId
LOCAL oSecrets
LOCAL oJson
LOCAL oJsonSecret
nSuccess := 0
// This example requires the Chilkat API to have been previously unlocked.
// See Global Unlock Sample for sample code.
// The bootstrap secret will contain the following information:
// Azure Tenant ID
// Azure Client ID
// Azure Client Secret
// See following examples for setting up a bootstrap secret in memory,
// or in the local manager (Windows Credentials Manager or Apple Keychain)
// Setup Bootstrap Secret in Local Manager
// Setup Bootstrap Secret in Memory
oBootstrap := CreateObject("Chilkat.Secrets")
// Set the location of the bootstrap secret.
// Can be "local_manager" or "memory", depending on how you setup the bootstrap secret.
// ---------------------------------------------------------------------------------------------
// If your operating system is NOT Windows or MacOS/iOS, then change "local_manager" to "memory"
// You can also, if desired, use "memory" on Windows and MacOS/iOS if your bootstrap secret was previously setup in memory.
// ---------------------------------------------------------------------------------------------
oBootstrap:Location := "local_manager"
// Specify the bootstrap secret to be used.
oBsId := CreateObject("Chilkat.JsonObject")
oBsId:UpdateString("appName", "azure_bs")
oBsId:UpdateString("service", "Example")
oBsId:UpdateString("username", "Joe")
// ----------------------------------------------------
oSecrets := CreateObject("Chilkat.Secrets")
oSecrets:Location := "azure_key_vault"
nSuccess := oSecrets:SetBootstrapSecret(oBsId, oBootstrap)
IF (nSuccess == 0)
? oSecrets:LastErrorText
oBootstrap:destroy()
oBsId:destroy()
oSecrets:destroy()
RETURN
ENDIF
// ----
// Specify the name of the secret.
// service and username are required.
// appName and domain are optional.
// Note: The values are arbitrary and can be anything you want.
oJson := CreateObject("Chilkat.JsonObject")
oJson:UpdateString("appName", "MyApp")
oJson:UpdateString("service", "OAuth2")
oJson:UpdateString("domain", "onedrive")
oJson:UpdateString("username", "matt")
// For Azure Key Vault, we also need to specify the name of the vault where the secret is to be stored.
// Replace "kvChilkat" with the name of your key vault.
oJson:UpdateString("vaultName", "kvChilkat")
// Get the secret to be stored.
oJsonSecret := CreateObject("Chilkat.JsonObject")
nSuccess := oJsonSecret:LoadFile("qa_data/tokens/oneDrive.json")
IF (nSuccess == 0)
? oJsonSecret:LastErrorText
oBootstrap:destroy()
oBsId:destroy()
oSecrets:destroy()
oJson:destroy()
oJsonSecret:destroy()
RETURN
ENDIF
// Create or update the secret.
nSuccess := oSecrets:UpdateSecretJson(oJson, oJsonSecret)
IF (nSuccess == 0)
? oSecrets:LastErrorText
oBootstrap:destroy()
oBsId:destroy()
oSecrets:destroy()
oJson:destroy()
oJsonSecret:destroy()
RETURN
ENDIF
? "Success."
// Here you can see the secret that was created:
// 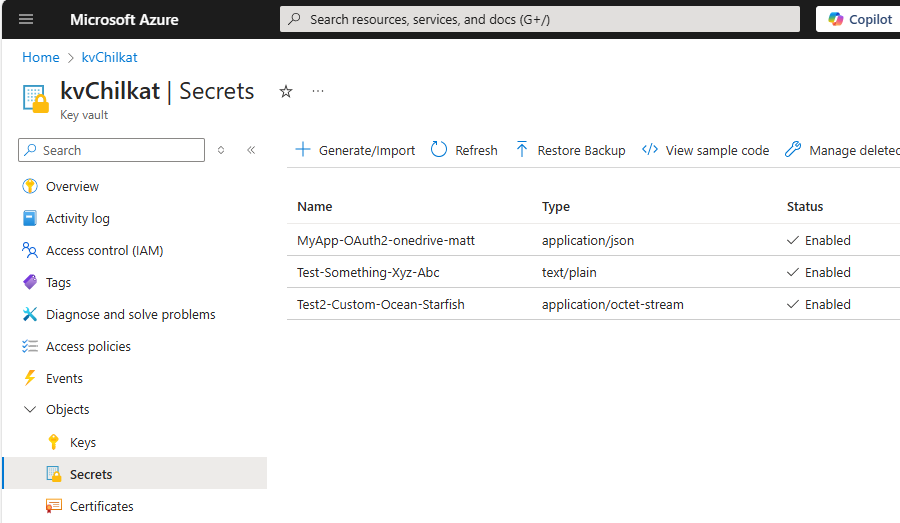 oBootstrap:destroy()
oBsId:destroy()
oSecrets:destroy()
oJson:destroy()
oJsonSecret:destroy()