Rust
Rust
Get OAuth2 Access Token for Azure Registered App
See more OAuth2 Examples
Demonstrates how to get OAuth2 access token for an Azure Registered App from a desktop application or script. This example demonstrates the OAuth2 authorization flow.This example requires Chilkat v10.1.2 or greater.
Chilkat Rust Downloads
// To further clarify, see OAuth 2.0 Authorization Flow

let oauth2 = chilkat::OAuth2::new();

// This should be the port in the localhost callback URL for your app.
// The callback URL would look like "http://localhost:3017/" if the port number is 3017.
oauth2.set_listen_port(3017);

// ----------------------------------------------------------------------------------------------------------
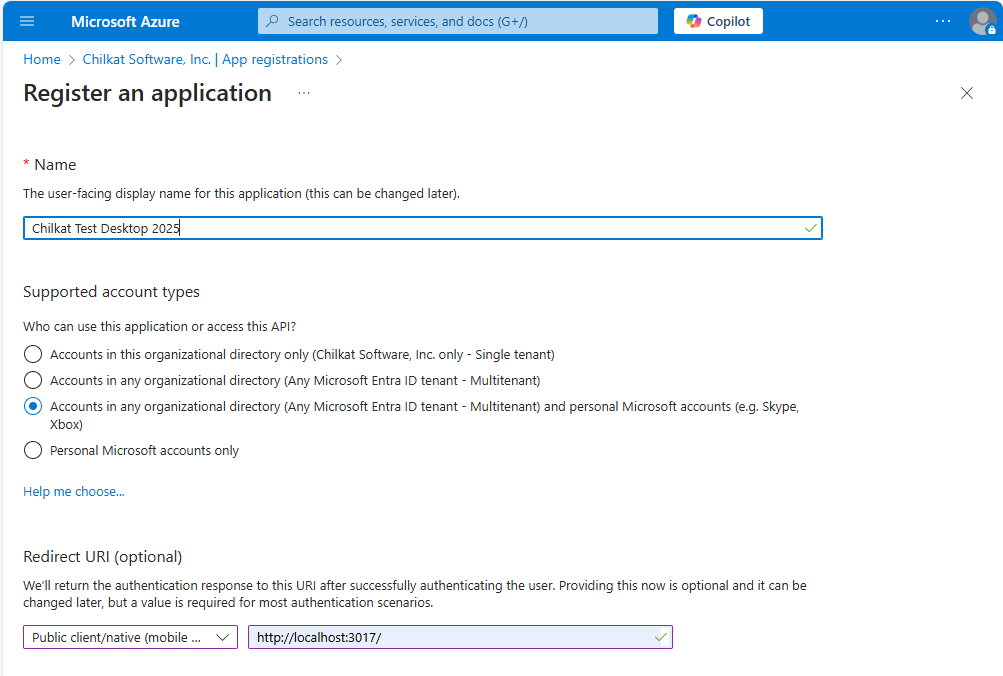
// The screenshot at the bottom of this page shows how we created the Azure App Registration for this example.
// ----------------------------------------------------------------------------------------------------------

// Note: The endpoint depends on the Azure App Registration.
// See How to Choose the Correct Endpoints for your Azure App Registration
oauth2.set_authorization_endpoint("https://login.microsoftonline.com/common/oauth2/v2.0/authorize");
oauth2.set_token_endpoint("https://login.microsoftonline.com/common/oauth2/v2.0/token");

// Replace these with actual values.
oauth2.set_client_id("CLIENT_ID");

// This is for Require Proof Key for Code Exchange (PKCE)
// See OAuth2 PKCE Explained
oauth2.set_code_challenge(true);
oauth2.set_code_challenge_method("S256");

// Provide a SPACE separated list of scopes.
// See https://developer.microsoft.com/en-us/graph/docs/authorization/permission_scopes

// Important: To get a refresh token in the final response, ask for "offline_access" scope
oauth2.set_scope("openid profile offline_access user.readwrite mail.readwrite mail.send files.readwrite");

// Begin the OAuth2 three-legged flow.  This returns a URL that should be loaded in a browser.
let Ok(url) = oauth2.start_auth() else {
    println!("{}", oauth2.last_error_text());
    return;
};

// Launch the default browser on the system and navigate to the url.
// The LaunchBrowser method was added in Chilkat v10.1.2.
if oauth2.launch_browser(&url).is_err() {
    println!("{}", oauth2.last_error_text());
    return;
}

// Wait for the user to approve or deny authorization in the browser.
let mut num_ms_waited = 0;
while (num_ms_waited < 90000) && (oauth2.auth_flow_state() < 3) {
    oauth2.sleep_ms(100);
    num_ms_waited = num_ms_waited + 100;
}

// If the browser does not respond within the specified time, AuthFlowState will be:
//
// 1: Waiting for Redirect – The OAuth2 background thread is waiting for the browser's redirect request.
// 2: Waiting for Final Response – The thread is awaiting the final access token response.
// In either case, cancel the background task initiated by StartAuth.

if oauth2.auth_flow_state() < 3 {
    let _ = oauth2.cancel();
    println!("No response from the browser!");
    return;
}

// Check AuthFlowState to determine if authorization was granted, denied, or failed:
//
// 3: Success – OAuth2 flow completed, the background thread exited, and the successful response is in AccessTokenResponse.
// 4: Access Denied – OAuth2 flow completed, the background thread exited, and the error response is in AccessTokenResponse.
// 5: Failure – OAuth2 flow failed before completion, the background thread exited, and error details are in FailureInfo.

if oauth2.auth_flow_state() == 5 {
    println!("OAuth2 failed to complete.");
    println!("{}", oauth2.failure_info());
    return;
}

if oauth2.auth_flow_state() == 4 {
    println!("OAuth2 authorization was denied.");
    println!("{}", oauth2.access_token_response());
    return;
}

if oauth2.auth_flow_state() != 3 {
    println!("Unexpected AuthFlowState:{}", oauth2.auth_flow_state());
    return;
}

println!("OAuth2 authorization granted!");
println!("Access Token = {}", oauth2.access_token());

// When the token is near expiration, your app can refresh as shown here:
// Refresh Expiring OAuth2 Access Token for Azure Registered App

// Get the full JSON response:
let json = chilkat::JsonObject::new();
let _ = json.load(&oauth2.access_token_response());
json.set_emit_compact(false);

// The JSON response looks like this:

// {
//   "token_type": "Bearer",
//   "scope": "User.Read Mail.ReadWrite Mail.Send",
//   "expires_in": 3600,
//   "ext_expires_in": 0,
//   "access_token": "EwBAA8l6B...",
//   "refresh_token": "MCRMdbe...",
//   "id_token": "eyJ0eXA..."
// }

// If an "expires_on" member does not exist, then add the JSON member by
// getting the current system date/time and adding the "expires_in" seconds.
// This way we'll know when the token expires.
if !json.has_member("expires_on") {
    let dt_expire = chilkat::DateTime::new();
    let _ = dt_expire.set_from_current_system_time();
    let _ = dt_expire.add_seconds(json.int_of("expires_in"));
    let _ = json.append_string("expires_on", &dt_expire.get_as_unix_time_str(false).unwrap_or_default());
}

println!("{}", json.emit().unwrap_or_default());

// Save the JSON to a file for future requests.
let fac = chilkat::FileAccess::new();
let _ = fac.write_entire_text_file("qa_data/tokens/_myAzureApp.json", &json.emit().unwrap_or_default(), "utf-8", false);

// This is a screenshot of how we created the Azure App for this example:
//