Rust Requires Chilkat v11.0.0+
Rust
ETrade OAuth1 Authorization (3-legged) Step 1
See more ETrade Examples
Demonstrates the first step in 3-legged OAuth1 authorization for the ETrade REST API. This example sends an HTTP request to the "request token URL" to get a request token that begins the OAuth1 process. (See https://apisb.etrade.com/docs/api/authorization/request_token.html )This example uses the sandbox request token URL. The live request token URL would be "https://api.etrade.com/oauth/request_token".
Chilkat Rust Downloads
// This requires the Chilkat API to have been previously unlocked.
// See Global Unlock Sample for sample code.

let consumer_key = "ETRADE_CONSUMER_KEY".to_string();
let consumer_secret = "ETRADE_CONSUMER_SECRET".to_string();

// Note: This example uses the sandbox request token URL.
// The live Get Request Token Request URL is:
// https://api.etrade.com/oauth/request_token
// This example will use the Sandbox Token Request URL:
let request_token_url = "https://apisb.etrade.com/oauth/request_token".to_string();

let http = chilkat::Http::new();
let _ = true;

http.set_o_auth1(true);
http.set_o_auth_consumer_key(&consumer_key);
http.set_o_auth_consumer_secret(&consumer_secret);
http.set_o_auth_callback("oob");

let resp = chilkat::HttpResponse::new();
if http.http_no_body("GET", &request_token_url, &resp).is_err() {
    println!("{}", http.last_error_text());
    return;
}

// If successful, the resp.BodyStr contains something like this:
// oauth_token=-Wa_KwAAAAAAxfEPAAABV8Qar4Q&oauth_token_secret=OfHY4tZBX2HK4f7yIw76WYdvnl99MVGB&oauth_callback_confirmed=true
println!("{}", resp.body_str());

let hash_tab = chilkat::Hashtable::new();
let _ = hash_tab.add_query_params(&resp.body_str());

let request_token = hash_tab.lookup_str("oauth_token").unwrap_or_default();
let request_token_secret = hash_tab.lookup_str("oauth_token_secret").unwrap_or_default();
http.set_o_auth_token_secret(&request_token_secret);

println!("oauth_token = {}", request_token);
println!("oauth_token_secret = {}", request_token_secret);

// Save this request token for the next step..
let json = chilkat::JsonObject::new();
let _ = json.append_string("oauth_token", &request_token);
let _ = json.append_string("oauth_token_secret", &request_token_secret);

let fac = chilkat::FileAccess::new();
let _ = fac.write_entire_text_file("qa_data/tokens/etrade_request_token.json", &json.emit().unwrap_or_default(), "utf-8", false);

// ---------------------------------------------------------------------------

// The next step is to form a URL to send to the authorizeUrl
// This is an HTTP GET that we load into a popup browser.
let authorize_url = "https://us.etrade.com/e/t/etws/authorize".to_string();

let sb_url_for_browser = chilkat::StringBuilder::new();
let _ = sb_url_for_browser.append(&authorize_url);
let _ = sb_url_for_browser.append("?key=");
let _ = sb_url_for_browser.append(&consumer_key);
let _ = sb_url_for_browser.append("&token=");
let _ = sb_url_for_browser.append(&request_token);
let url = sb_url_for_browser.get_as_string().unwrap_or_default();

// Launch the system's default browser navigated to the URL.
let oauth2 = chilkat::OAuth2::new();
if oauth2.launch_browser(&url).is_err() {
    println!("{}", oauth2.last_error_text());
    return;
}

// The ETrade account owner will login and grant access to the application.
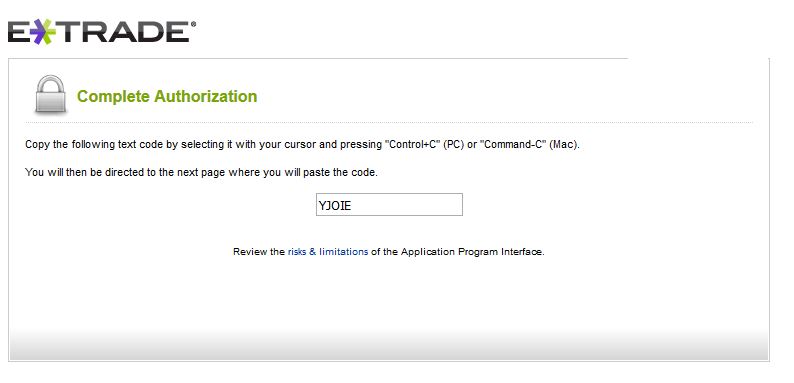
// A short verifier code will be displayed (as shown below), and this must be copy-and-pasted
// into the next step to Complete the 3-legged OAuth1 Authorization

// Note: The browser will NOT automatically direct you to the next page.
// You should copy the verifier code, close the browser, and then paste the verifier
// code into your application.

//