Rust
Rust
Azure Key Vault - Create or Update a JSON Secret
See more Secrets Examples
Demonstrates how to create or update a JSON secret stored in the Azure Key Vault.Note: This example requires Chilkat v10.1.0 or later.
Chilkat Rust Downloads
// This example requires the Chilkat API to have been previously unlocked.
// See Global Unlock Sample for sample code.

// The bootstrap secret will contain the following information:

// Azure Tenant ID
// Azure Client ID
// Azure Client Secret

// See following examples for setting up a bootstrap secret in memory,
// or in the local manager (Windows Credentials Manager or Apple Keychain)
// Setup Bootstrap Secret in Local Manager
// Setup Bootstrap Secret in Memory
let bootstrap = chilkat::Secrets::new();

// Set the location of the bootstrap secret.
// Can be "local_manager" or "memory", depending on how you setup the bootstrap secret.
// ---------------------------------------------------------------------------------------------
// If your operating system is NOT Windows or MacOS/iOS, then change "local_manager" to "memory"
// You can also, if desired, use "memory" on Windows and MacOS/iOS if your bootstrap secret was previously setup in memory.
// ---------------------------------------------------------------------------------------------
bootstrap.set_location("local_manager");

// Specify the bootstrap secret to be used.
let bs_id = chilkat::JsonObject::new();
let _ = bs_id.update_string("appName", "azure_bs");
let _ = bs_id.update_string("service", "Example");
let _ = bs_id.update_string("username", "Joe");

// ----------------------------------------------------
let secrets = chilkat::Secrets::new();

secrets.set_location("azure_key_vault");
if secrets.set_bootstrap_secret(&bs_id, &bootstrap).is_err() {
    println!("{}", secrets.last_error_text());
    return;
}

// ----
// Specify the name of the secret.
// service and username are required.
// appName and domain are optional.
// Note: The values are arbitrary and can be anything you want.
let json = chilkat::JsonObject::new();
let _ = json.update_string("appName", "MyApp");
let _ = json.update_string("service", "OAuth2");
let _ = json.update_string("domain", "onedrive");
let _ = json.update_string("username", "matt");

// For Azure Key Vault, we also need to specify the name of the vault where the secret is to be stored.
// Replace "kvChilkat" with the name of your key vault.
let _ = json.update_string("vaultName", "kvChilkat");

// Get the secret to be stored.
let json_secret = chilkat::JsonObject::new();
if json_secret.load_file("qa_data/tokens/oneDrive.json").is_err() {
    println!("{}", json_secret.last_error_text());
    return;
}

// Create or update the secret.
if secrets.update_secret_json(&json, &json_secret).is_err() {
    println!("{}", secrets.last_error_text());
    return;
}

println!("Success.");

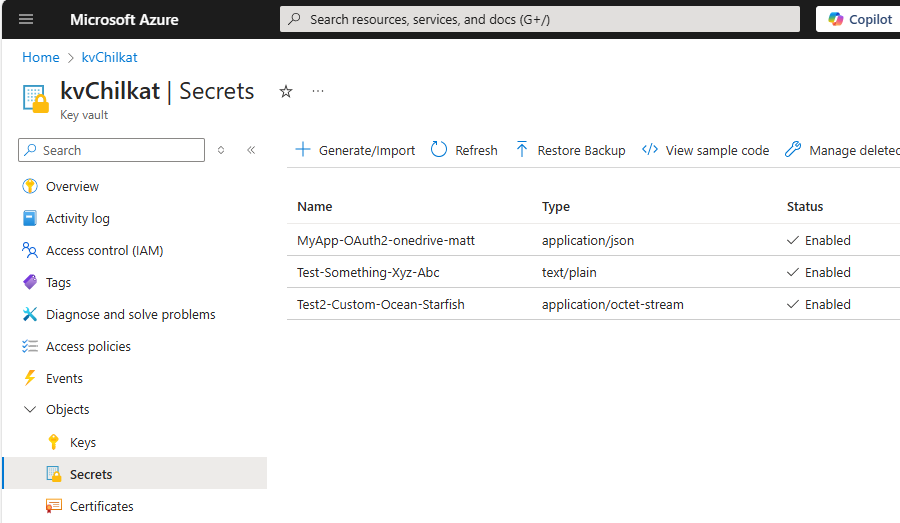
// Here you can see the secret that was created:

//