Lua Requires Chilkat v11.0.0+
Lua
ETrade OAuth1 Authorization (3-legged) Step 1
See more ETrade Examples
Demonstrates the first step in 3-legged OAuth1 authorization for the ETrade REST API. This example sends an HTTP request to the "request token URL" to get a request token that begins the OAuth1 process. (See https://apisb.etrade.com/docs/api/authorization/request_token.html )This example uses the sandbox request token URL. The live request token URL would be "https://api.etrade.com/oauth/request_token".
Chilkat Lua Downloads
local chilkat = require("chilkat")

-- This requires the Chilkat API to have been previously unlocked.
-- See Global Unlock Sample for sample code.

local consumerKey = "ETRADE_CONSUMER_KEY"
local consumerSecret = "ETRADE_CONSUMER_SECRET"

-- Note: This example uses the sandbox request token URL.
-- The live Get Request Token Request URL is:
-- https://api.etrade.com/oauth/request_token
-- This example will use the Sandbox Token Request URL:
local requestTokenUrl = "https://apisb.etrade.com/oauth/request_token"

local http = chilkat.Http.new()
local success = true

http.oauth1 = true
http.oauth_consumer_key = consumerKey
http.oauth_consumer_secret = consumerSecret
http.oauth_callback = "oob"

local resp = chilkat.HttpResponse.new()
success = http:http_no_body("GET", requestTokenUrl, resp)
if not success then
    print(http.last_error_text)
    return
end

-- If successful, the resp.BodyStr contains something like this:
-- oauth_token=-Wa_KwAAAAAAxfEPAAABV8Qar4Q&oauth_token_secret=OfHY4tZBX2HK4f7yIw76WYdvnl99MVGB&oauth_callback_confirmed=true
print(resp.body_str)

local hashTab = chilkat.Hashtable.new()
hashTab:add_query_params(resp.body_str)

local requestToken = hashTab:lookup_str("oauth_token")
local requestTokenSecret = hashTab:lookup_str("oauth_token_secret")
http.oauth_token_secret = requestTokenSecret

print("oauth_token = " .. requestToken)
print("oauth_token_secret = " .. requestTokenSecret)

-- Save this request token for the next step..
local json = chilkat.JsonObject.new()
json:append_string("oauth_token", requestToken)
json:append_string("oauth_token_secret", requestTokenSecret)

local fac = chilkat.FileAccess.new()
fac:write_entire_text_file("qa_data/tokens/etrade_request_token.json", json:emit(), "utf-8", false)

-- ---------------------------------------------------------------------------

-- The next step is to form a URL to send to the authorizeUrl
-- This is an HTTP GET that we load into a popup browser.
local authorizeUrl = "https://us.etrade.com/e/t/etws/authorize"

local sbUrlForBrowser = chilkat.StringBuilder.new()
sbUrlForBrowser:append(authorizeUrl)
sbUrlForBrowser:append("?key=")
sbUrlForBrowser:append(consumerKey)
sbUrlForBrowser:append("&token=")
sbUrlForBrowser:append(requestToken)
local url = sbUrlForBrowser:get_as_string()

-- Launch the system's default browser navigated to the URL.
local oauth2 = chilkat.OAuth2.new()
success = oauth2:launch_browser(url)
if not success then
    print(oauth2.last_error_text)
    return
end

-- The ETrade account owner will login and grant access to the application.
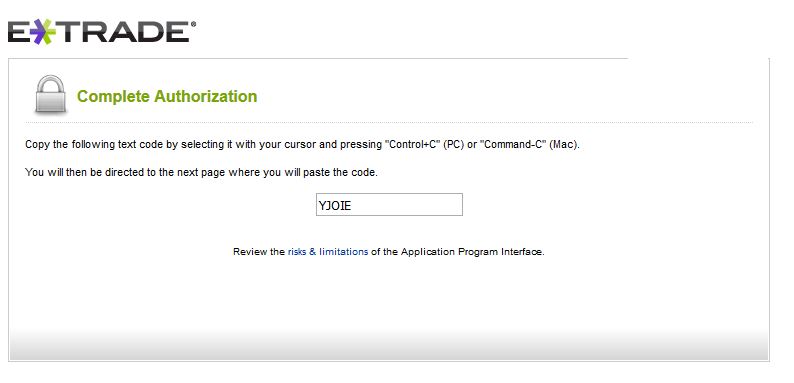
-- A short verifier code will be displayed (as shown below), and this must be copy-and-pasted
-- into the next step to Complete the 3-legged OAuth1 Authorization

-- Note: The browser will NOT automatically direct you to the next page.
-- You should copy the verifier code, close the browser, and then paste the verifier
-- code into your application.

--