Lua Requires Chilkat v9.5.0.96+
Lua
Create CAdES p7m using AWS KMS to Sign in the Cloud
See more Signing in the Cloud Examples
Demonstrates how to create a CAdES p7m, using AWS KMS. The signing of the hash happens in the Cloud on AWS KMS. Everything else regarding the creation of CAdES happens locally within Chilkat.Chilkat Lua Downloads
local chilkat = require("chilkat")
-- This example assumes the Chilkat API to have been previously unlocked.
-- See Global Unlock Sample for sample code.
-- Load the certificate used for signing. The certificate's private key is stored in AWS KMS
-- However, we still need the certificate locally (without private key).
local cert = chilkat.Cert.new()
local success = cert:load_from_file("qa_data/certs/myCert.cer")
if not success then
print(cert.last_error_text)
return
end
-- Here's a screenshot showing the key ID of a private key in AWS KMS:
-- 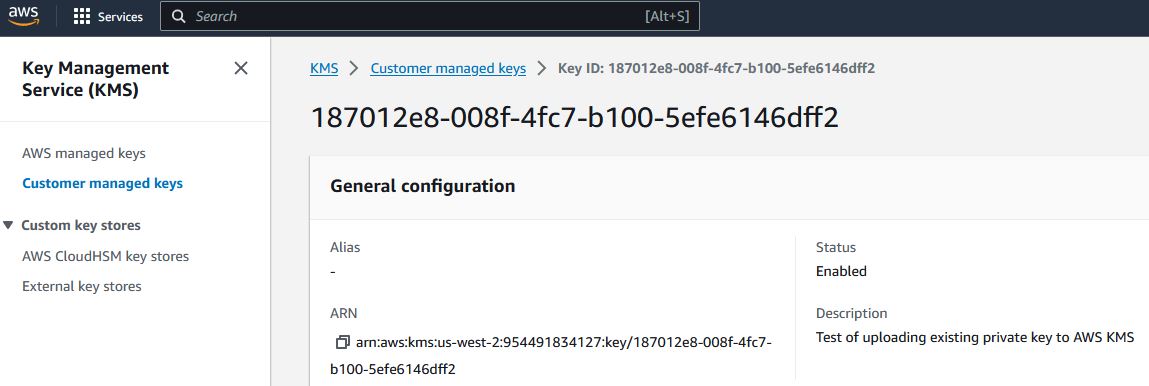 -- To sign using AWS KMS,
-- add the following lines of code to specify your AWS authentication credentials,
-- and the ID of the KMS private key.
local jsonAwsKms = chilkat.JsonObject.new()
-- Set the "service" equal to "aws_kms" to tell Chilkat to use AWS KMS for signing.
jsonAwsKms:update_string("service", "aws_kms")
jsonAwsKms:update_string("access_key", "ACCESS_KEY")
jsonAwsKms:update_string("secret_key", "SECRET_KEY")
-- Make sure to specify the correct region for your case.
jsonAwsKms:update_string("region", "us-west-2")
-- In the above screenshot, our key ID is "187012e8-008f-4fc7-b100-5efe6146dff2". You will use your key ID.
jsonAwsKms:update_string("key_id", "187012e8-008f-4fc7-b100-5efe6146dff2")
success = cert:set_cloud_signer(jsonAwsKms)
local crypt = chilkat.Crypt2.new()
success = crypt:set_signing_cert(cert)
if not success then
print(crypt.last_error_text)
return
end
-- The CadesEnabled property applies to all methods that create PKCS7 signatures.
-- To create a CAdES-BES signature, set this property equal to true.
crypt.cades_enabled = true
crypt.hash_algorithm = "sha256"
local signedAttrs = chilkat.JsonObject.new()
signedAttrs:update_int("contentType", 1)
signedAttrs:update_int("signingTime", 1)
signedAttrs:update_int("messageDigest", 1)
signedAttrs:update_int("signingCertificateV2", 1)
crypt.signing_attributes = signedAttrs:emit()
-- You can sign any type of file..
local inputXmlPath = "qa_data/e-Invoice.xml"
local outputP7mPath = "qa_output/signed.p7m"
-- Create the CAdES-BES attached signature, which contains the original data.
-- Chilkat will build the .p7m locally, but will (internally) use ARSS
-- to do the RSA signing remotely.
success = crypt:create_p7_m(inputXmlPath, outputP7mPath)
if not success then
print(crypt.last_error_text)
return
end
print("Success.")