Java Requires Chilkat v10.1.2+
Chilkat2 Java
HMRC OAuth2 Access Token
See more OAuth2 Examples
Demonstrates how to get an HMRC OAuth2 access token from a desktop (installed) application or script. This example gets an HMRC MTD VAT read/write access token.Chilkat Java Downloads
import com.chilkatsoft.chilkat2.ChilkatException;
import com.chilkatsoft.chilkat2.DateTime;
import com.chilkatsoft.chilkat2.FileAccess;
import com.chilkatsoft.chilkat2.JsonObject;
import com.chilkatsoft.chilkat2.OAuth2;

public class ChilkatExample {

    public static void main(String[] args) {
        // To further clarify, see OAuth 2.0 Authorization Flow

        OAuth2 oauth2 = new OAuth2();

        // This should be the port in the localhost callback URL for your app.
        // Important: Make sure the callback URI in your HMRC developer app
        // is exactly "http://localhost:3017/".  Don't forget the ending "/" char.
        // The callback URL would look like "http://localhost:3017/" if the port number is 3017.

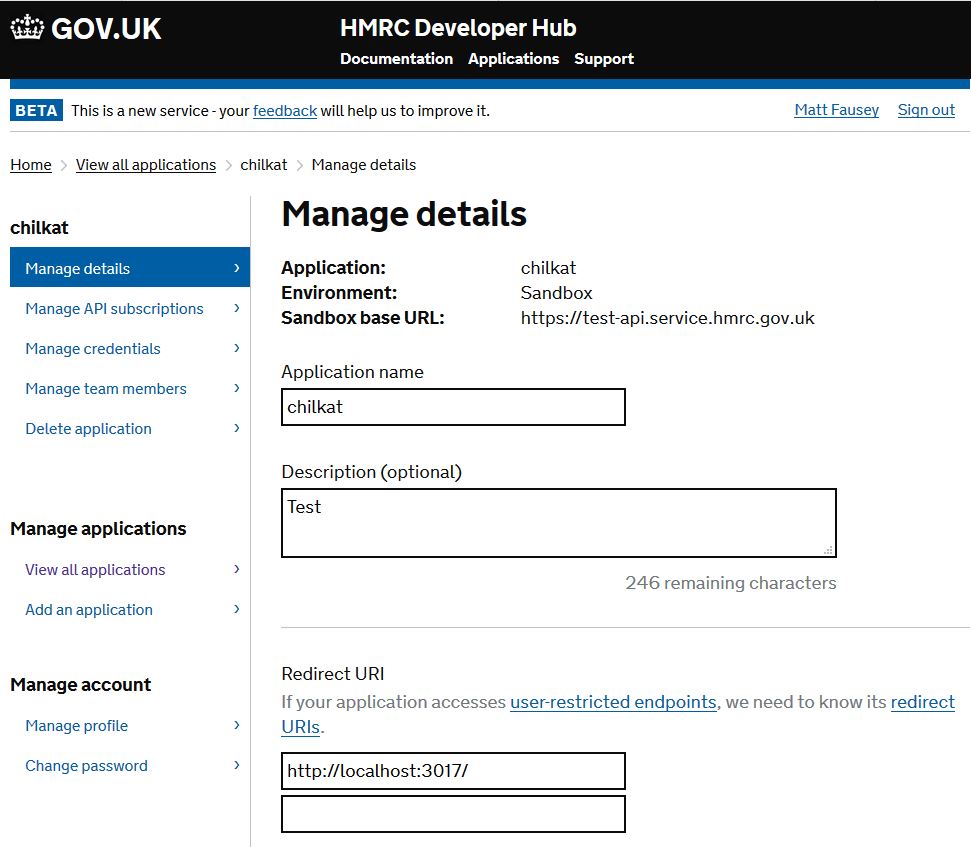
        // IMPORTANT: Don't forget to setup your HMRC application to use the Redirect URI "http://localhost:3017/" as shown
        // here: Configure Redirect URI for HMRC application
        oauth2.setListenPort(3017);

        oauth2.setAuthorizationEndpoint("https://test-api.service.hmrc.gov.uk/oauth/authorize");
        oauth2.setTokenEndpoint("https://test-api.service.hmrc.gov.uk/oauth/token");

        // Replace with your actual client ID
        oauth2.setClientId("HMRC-CLIENT-ID");

        // The scopes are documented in the HMRC reference documentation for each API.
        // This example gets a read/write access token for the HMRC MTD VAT API.
        oauth2.setScope("read:vat write:vat");

        // Begin the OAuth2 Authorization code flow.  This returns a URL that should be loaded in a browser.
        String url;
        try {
            url = oauth2.startAuth();

            // Launch the default browser on the system and navigate to the url.
            // The LaunchBrowser method was added in Chilkat v10.1.2.
            oauth2.launchBrowser(url);
        } catch (ChilkatException e) {
            System.out.println(e.getLastErrorText());
            return;
        }

        // Wait for the user to approve or deny authorization in the browser.
        int numMsWaited = 0;
        while ((numMsWaited < 90000) && (oauth2.getAuthFlowState() < 3)) {
            oauth2.sleepMs(100);
            numMsWaited = numMsWaited + 100;
        }

        // If the browser does not respond within the specified time, AuthFlowState will be:
        //
        // 1: Waiting for Redirect – The OAuth2 background thread is waiting for the browser's redirect request.
        // 2: Waiting for Final Response – The thread is awaiting the final access token response.
        // In either case, cancel the background task initiated by StartAuth.

        if (oauth2.getAuthFlowState() < 3) {
            oauth2.cancel();
            System.out.println("No response from the browser!");
            return;
        }

        // Check AuthFlowState to determine if authorization was granted, denied, or failed:
        //
        // 3: Success – OAuth2 flow completed, the background thread exited, and the successful response is in AccessTokenResponse.
        // 4: Access Denied – OAuth2 flow completed, the background thread exited, and the error response is in AccessTokenResponse.
        // 5: Failure – OAuth2 flow failed before completion, the background thread exited, and error details are in FailureInfo.

        if (oauth2.getAuthFlowState() == 5) {
            System.out.println("OAuth2 failed to complete.");
            System.out.println(oauth2.getFailureInfo());
            return;
        }

        if (oauth2.getAuthFlowState() == 4) {
            System.out.println("OAuth2 authorization was denied.");
            System.out.println(oauth2.getAccessTokenResponse());
            return;
        }

        if (oauth2.getAuthFlowState() != 3) {
            System.out.println("Unexpected AuthFlowState:" + oauth2.getAuthFlowState());
            return;
        }

        System.out.println("OAuth2 authorization granted!");
        System.out.println("Access Token = " + oauth2.getAccessToken());

        // Get the full JSON response:
        JsonObject json = new JsonObject();
        json.load(oauth2.getAccessTokenResponse());
        json.setEmitCompact(false);
        System.out.println(json.emit());

        // The JSON response looks like this:

        // {
        //   "token_type": "Bearer",
        //   "scope": "user_impersonation",
        //   "expires_in": "3599",
        //   "ext_expires_in": "0",
        //   "expires_on": "1524783438",
        //   "not_before": "1524779538",
        //   "resource": "https://mydomain.api.crm.dynamics.com",
        //   "access_token": "...",
        //   "refresh_token": "...",
        //   "id_token": "..."
        // }

        // If an "expires_on" member does not exist, then add the JSON member by
        // getting the current system date/time and adding the "expires_in" seconds.
        // This way we'll know when the token expires.
        if (!json.hasMember("expires_on")) {
            DateTime dtExpire = new DateTime();
            dtExpire.setFromCurrentSystemTime();
            dtExpire.addSeconds(json.intOf("expires_in"));
            json.appendString("expires_on", dtExpire.getAsUnixTimeStr(false));
        }

        System.out.println(json.emit());

        // Save the JSON to a file for future requests.
        FileAccess fac = new FileAccess();
        fac.writeEntireTextFile("qa_data/tokens/hmrc.json", json.emit(), "utf-8", false);
    }
}