Java
Chilkat2 Java
Create CAdES p7m using AWS KMS to Sign in the Cloud
See more Signing in the Cloud Examples
Demonstrates how to create a CAdES p7m, using AWS KMS. The signing of the hash happens in the Cloud on AWS KMS. Everything else regarding the creation of CAdES happens locally within Chilkat.Note: This example requires Chilkat v9.5.0.96 or greater.
Chilkat Java Downloads
import com.chilkatsoft.chilkat2.Cert;
import com.chilkatsoft.chilkat2.ChilkatException;
import com.chilkatsoft.chilkat2.Crypt2;
import com.chilkatsoft.chilkat2.JsonObject;
public class ChilkatExample {
public static void main(String[] args) {
// This example assumes the Chilkat API to have been previously unlocked.
// See Global Unlock Sample for sample code.
// Load the certificate used for signing. The certificate's private key is stored in AWS KMS
// However, we still need the certificate locally (without private key).
Cert cert = new Cert();
try {
cert.loadFromFile("qa_data/certs/myCert.cer");
} catch (ChilkatException e) {
System.out.println(e.getLastErrorText());
return;
}
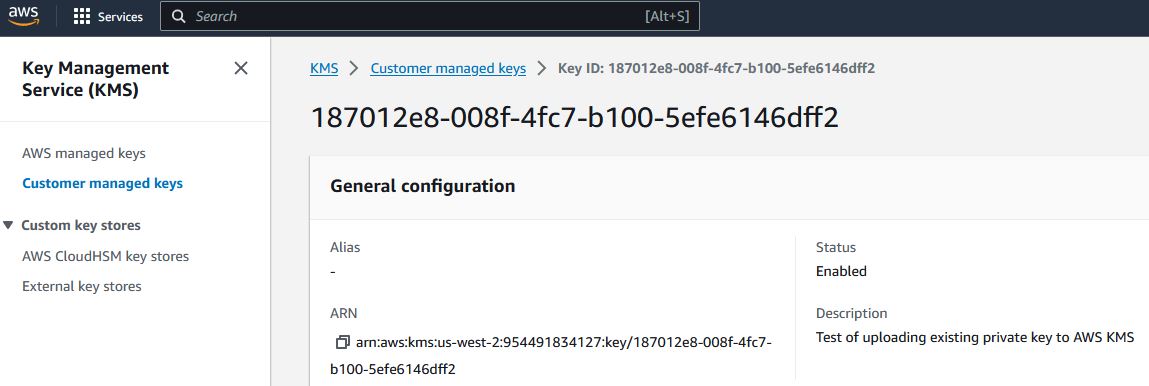
// Here's a screenshot showing the key ID of a private key in AWS KMS:
//  // To sign using AWS KMS,
// add the following lines of code to specify your AWS authentication credentials,
// and the ID of the KMS private key.
JsonObject jsonAwsKms = new JsonObject();
// Set the "service" equal to "aws_kms" to tell Chilkat to use AWS KMS for signing.
jsonAwsKms.updateString("service", "aws_kms");
jsonAwsKms.updateString("access_key", "ACCESS_KEY");
jsonAwsKms.updateString("secret_key", "SECRET_KEY");
// Make sure to specify the correct region for your case.
jsonAwsKms.updateString("region", "us-west-2");
// In the above screenshot, our key ID is "187012e8-008f-4fc7-b100-5efe6146dff2". You will use your key ID.
jsonAwsKms.updateString("key_id", "187012e8-008f-4fc7-b100-5efe6146dff2");
cert.setCloudSigner(jsonAwsKms);
Crypt2 crypt = new Crypt2();
try {
crypt.setSigningCert(cert);
} catch (ChilkatException e) {
System.out.println(e.getLastErrorText());
return;
}
// The CadesEnabled property applies to all methods that create PKCS7 signatures.
// To create a CAdES-BES signature, set this property equal to true.
crypt.setCadesEnabled(true);
crypt.setHashAlgorithm("sha256");
JsonObject signedAttrs = new JsonObject();
signedAttrs.updateInt("contentType", 1);
signedAttrs.updateInt("signingTime", 1);
signedAttrs.updateInt("messageDigest", 1);
signedAttrs.updateInt("signingCertificateV2", 1);
crypt.setSigningAttributes(signedAttrs.emit());
// You can sign any type of file..
String inputXmlPath = "qa_data/e-Invoice.xml";
String outputP7mPath = "qa_output/signed.p7m";
// Create the CAdES-BES attached signature, which contains the original data.
// Chilkat will build the .p7m locally, but will (internally) use ARSS
// to do the RSA signing remotely.
try {
crypt.createP7M(inputXmlPath, outputP7mPath);
} catch (ChilkatException e) {
System.out.println(e.getLastErrorText());
return;
}
System.out.println("Success.");
}
}